
EU Home Battery Networks Face Cyberattack Risk, Dutch Watchdog Warns
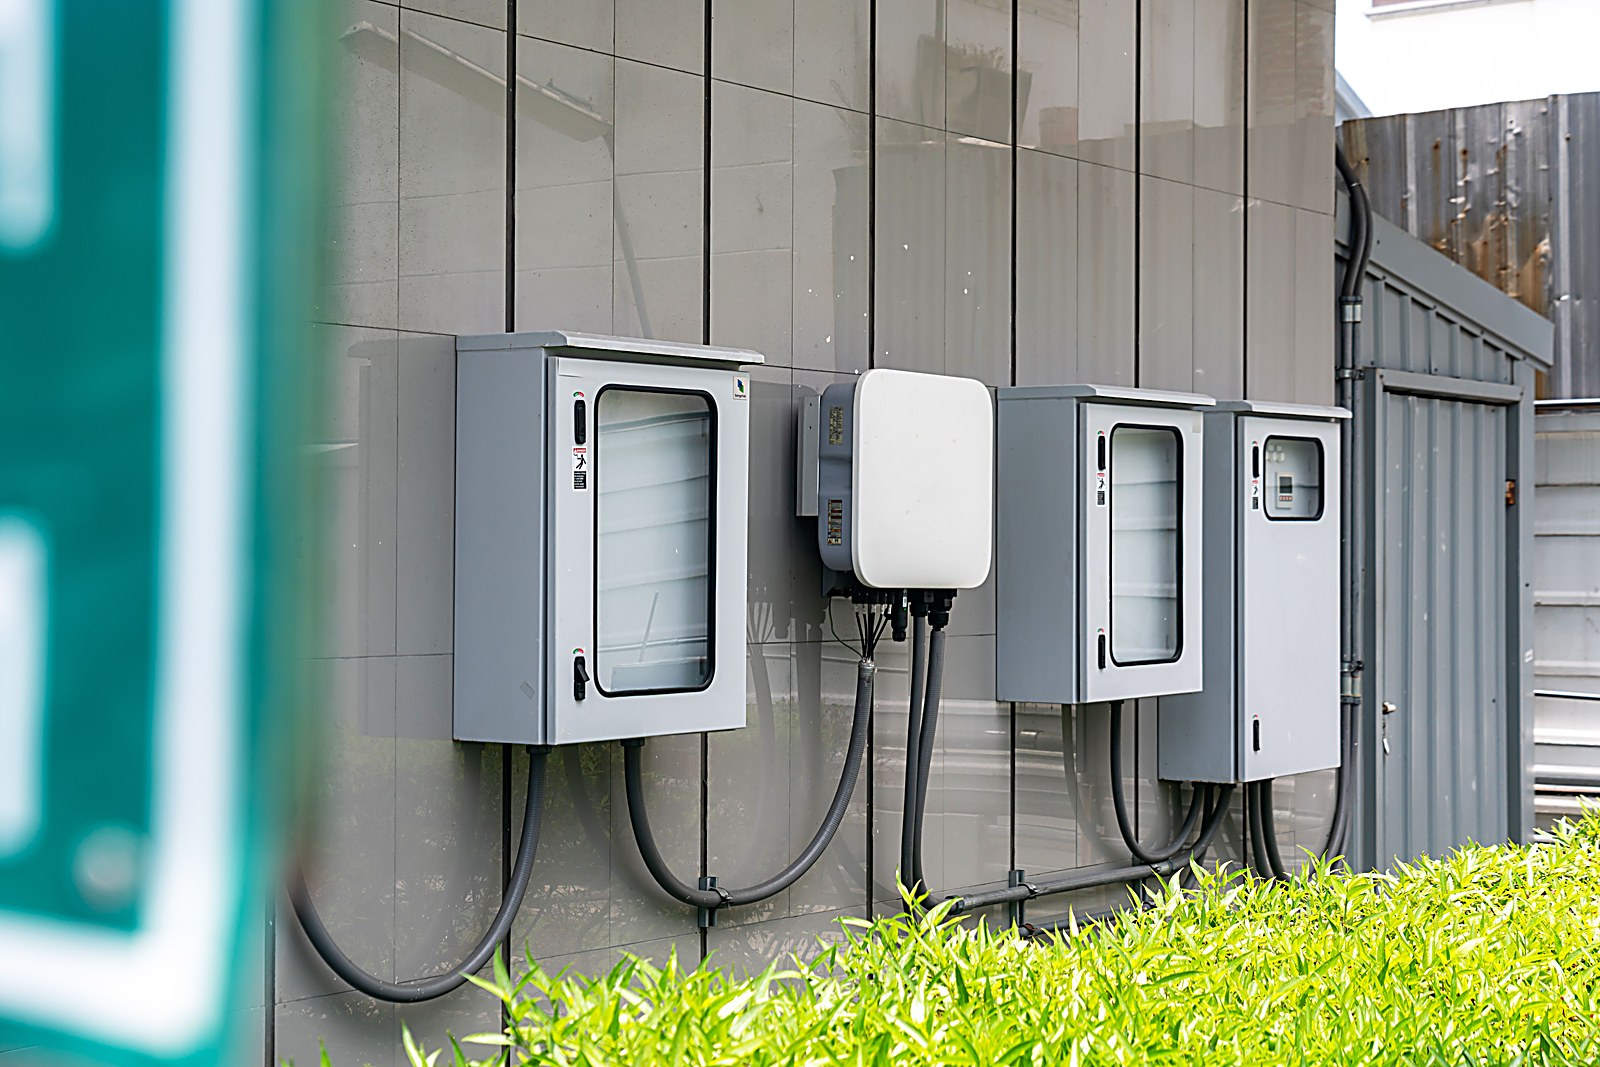
Europe’s rapid expansion of residential energy storage has created a cybersecurity blind spot that existing regulations were not designed to address, according to a report from the Netherlands’ digital infrastructure inspectorate.
The core problem lies in how current EU rules determine oversight. Whether an aggregator falls under the NIS2 cybersecurity directive depends on company size — not on the aggregate capacity being remotely managed. That means a small operator controlling gigawatts of distributed batteries and inverters may face no mandatory security scrutiny at all.
The Dutch report warns that a simultaneous disruption of that scale — estimated at up to 3 GW — could destabilize the broader European grid. The Netherlands has seen its combined fleet of heat pumps and EV chargers grow fivefold between 2019 and 2024, concentrating enormous load behind a handful of cloud platforms. A faulty firmware update or a targeted intrusion could disable thousands of connected devices in lockstep.
Researchers presenting at an energy security gathering in The Hague reinforced the concern, identifying more than 8,500 publicly reachable network systems across European solar and wind installations.
The Dutch regulator proposes three remedies: classify residential batteries, inverters and EV chargers as Class 2 critical products under the EU Cyber Resilience Act, requiring mandatory independent security audits; redefine NIS2 thresholds around managed grid capacity rather than company headcount; and reduce dependence on non-EU vendors capable of remotely influencing devices at significant scale.
If adopted, the reforms would shift the regulatory yardstick for smart-grid operators from corporate size to real-world grid influence.
Source: ESS News (pv magazine)
Become a member of 100 RE UA
Switching to 100% renewable energy in Ukraine is possible!